Nothing happens legally. No regulator penalises an organisation for lacking HITRUST certification. The consequences are commercial and contractual: breach of contract where certification is a stated obligation, loss of renewals, exclusion from RFPs, longer security reviews, a higher vendor risk rating and a weaker position if you suffer a breach.
Scenario 1: No customer has asked for it
If no contract, RFP or questionnaire mentions HITRUST, the consequence of not certifying is close to nil today. Your exposure is strategic: when the first enterprise healthcare buyer asks, you will be 5 to 15 months from a certificate. The sensible action is a readiness assessment so you know the gap and can quote a credible date.
Scenario 2: Your contract requires HITRUST and you miss the date
This is where real consequences sit. Typical contract language gives the vendor 12 to 24 months from signature to obtain certification. If you miss it:
| Consequence | How it typically plays out |
| Notice of non-compliance | Customer’s vendor management issues a formal finding |
| Cure period | Commonly 30 to 90 days to present a remediation plan |
| Enhanced oversight | Customer-led audits, additional questionnaires, on-site reviews at your cost |
| Commercial penalties | Fee holdbacks, service credits or withheld expansion |
| Termination right | Material breach clauses can be triggered |
| Renewal risk | Contract is put out to tender at the next term |
In practice, customers rarely terminate immediately. They escalate. But a vendor on a “watch list” does not win expansions.
What to do: communicate early, present a dated plan endorsed by your Authorized External Assessor, offer an interim deliverable such as a readiness report or an e1, and negotiate a revised date in writing.
Scenario 3: Your certification lapses
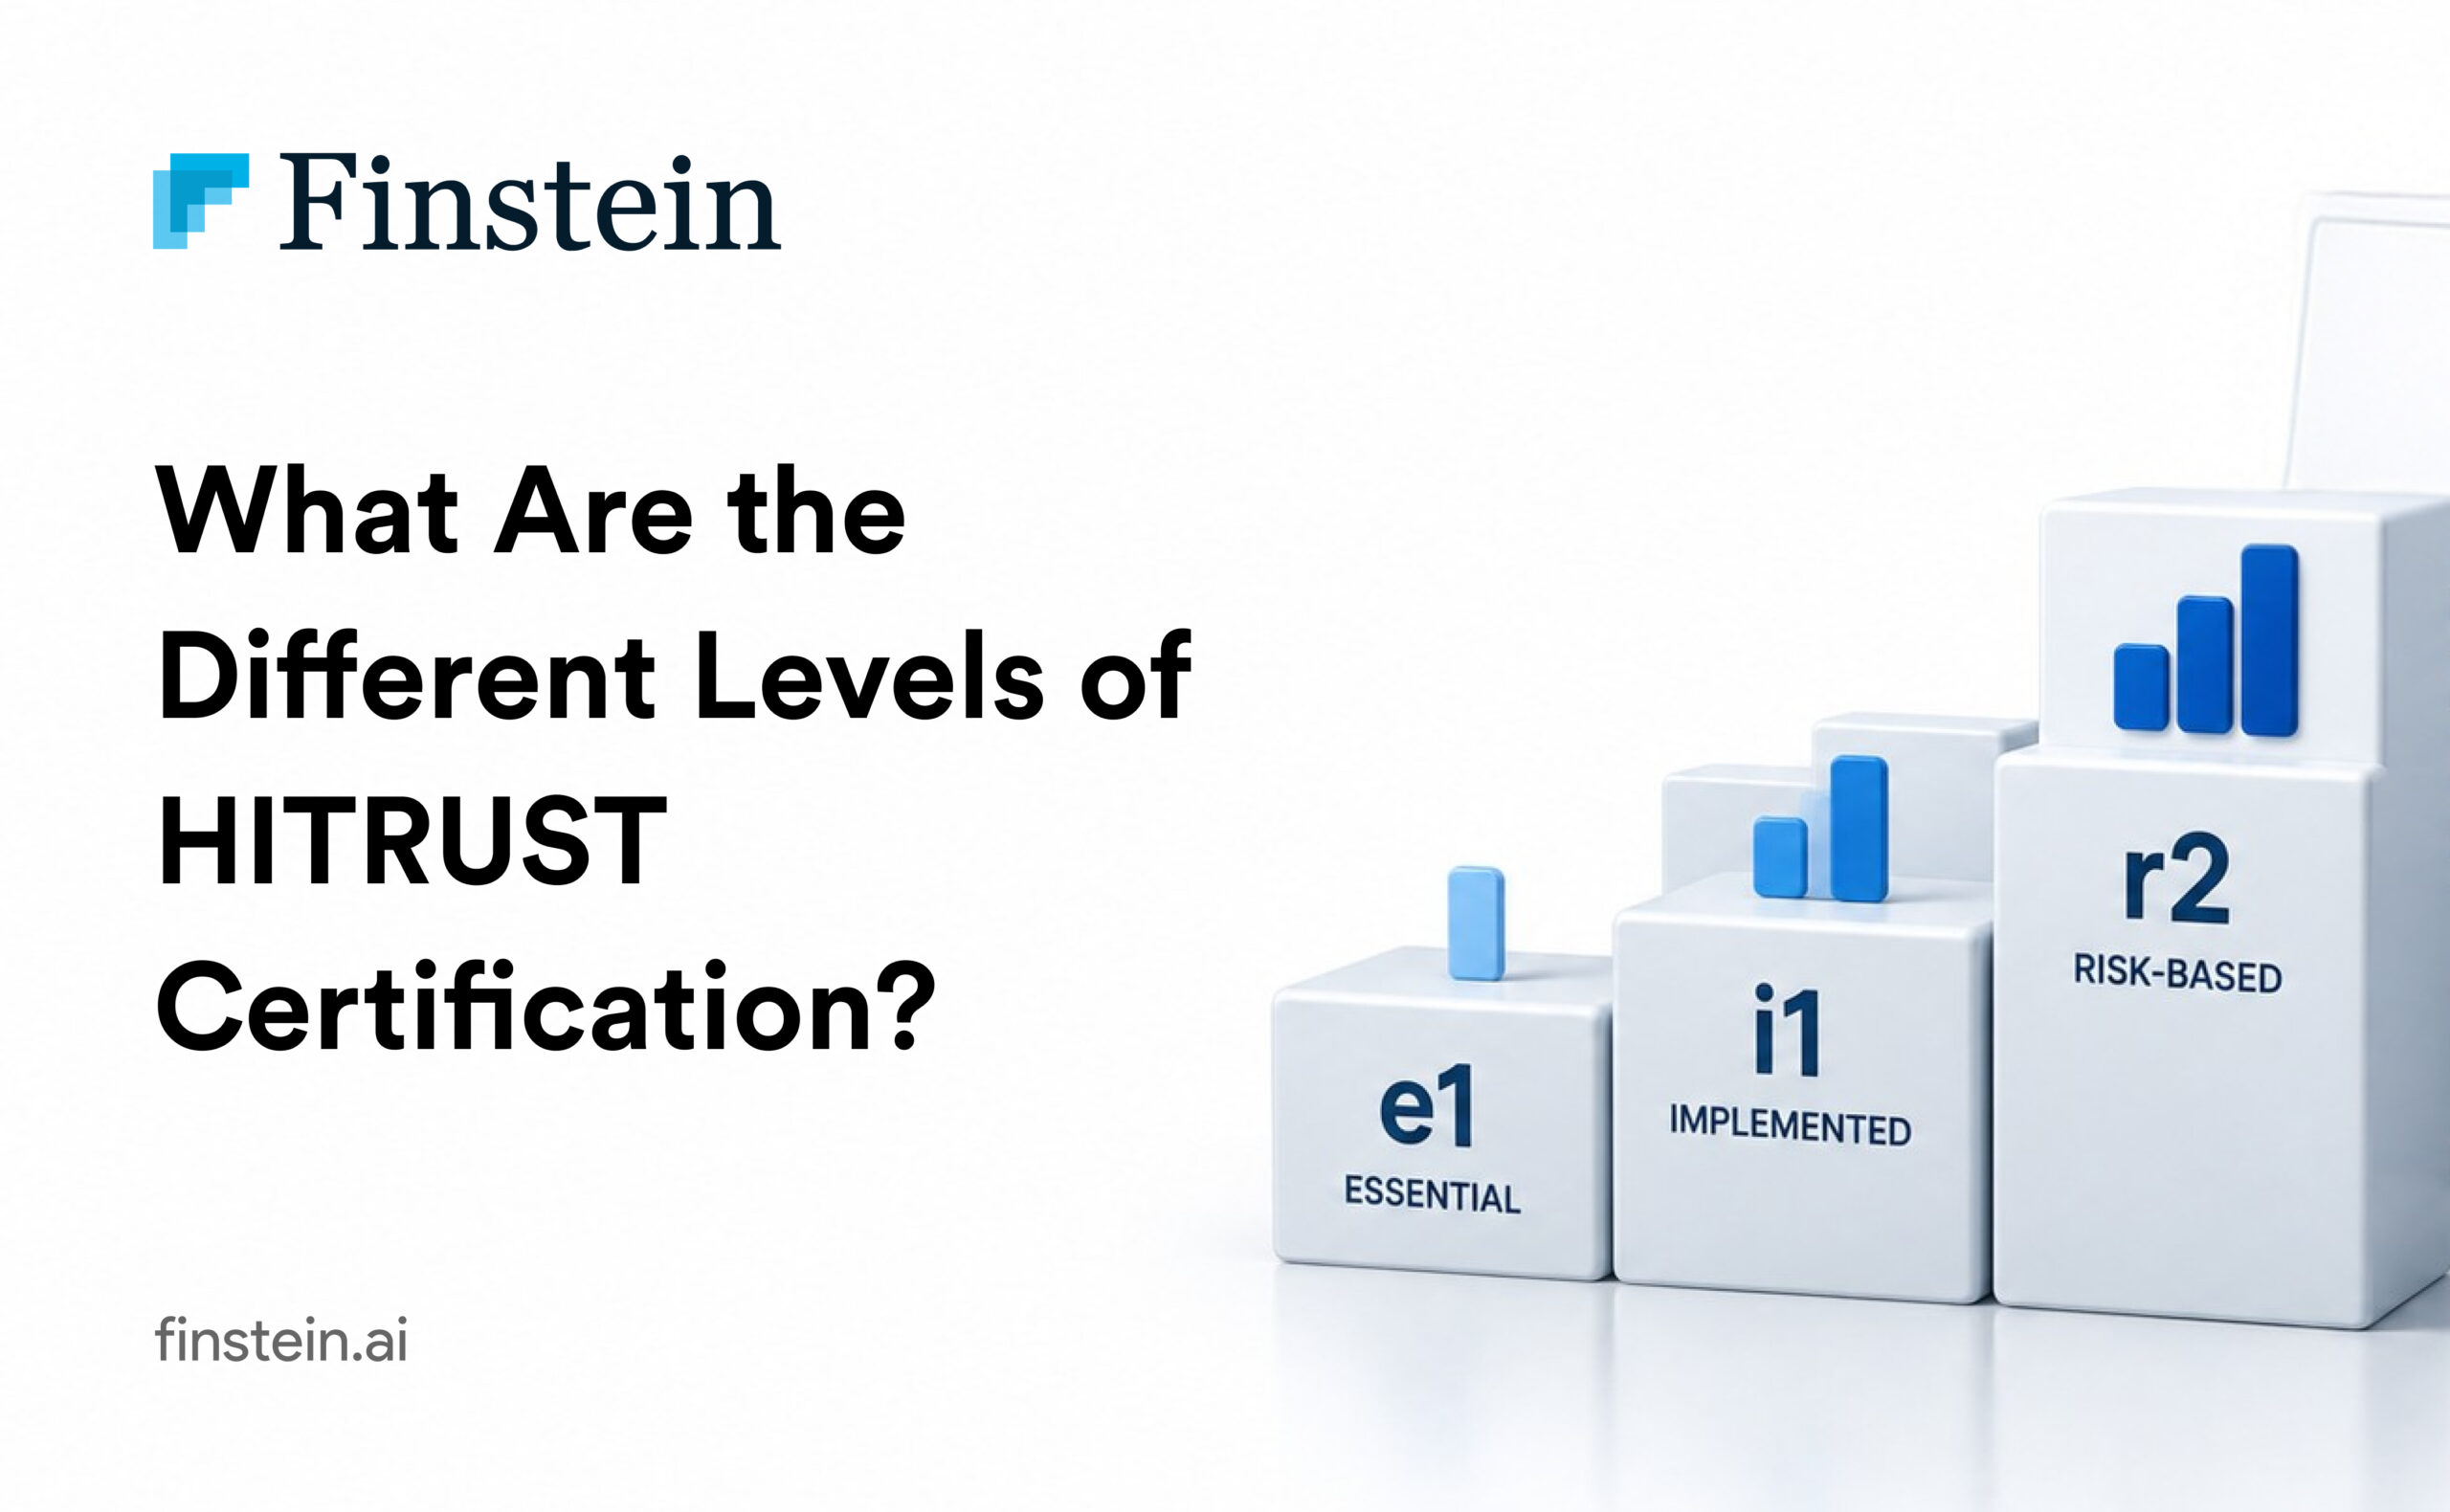
Certifications expire. e1 and i1 after one year, r2 after two years subject to the interim assessment. If you let it lapse:
- You can no longer represent yourself as HITRUST certified. Continuing to display the mark is a misrepresentation risk.
- Customers relying on your certification through HITRUST’s results sharing will see the status change.
- Contract clauses requiring you to “maintain” certification are breached.
- For r2, HITRUST offers a bridge certificate in defined circumstances to cover a short gap when recertification is in progress. It is not a substitute for planning. Confirm eligibility with HITRUST.
Scenario 4: You suffer a breach without certification
The absence of certification does not create liability by itself. It does remove useful defences:
- Regulatory. Under Public Law 116-321, HHS OCR must consider recognized security practices in place for the prior 12 months. Without independently validated evidence, that is harder to demonstrate.
- Litigation. Plaintiffs will test whether your security was reasonable. A maintained certification against a recognised framework is strong evidence.
- Insurance. Underwriters will scrutinise statements made on the application. A validated control environment reduces dispute risk.
- Customer confidence. Customers decide quickly whether to stay. Certified vendors have a documented baseline to point to.
The quieter consequences
Even without a contractual trigger, uncertified vendors selling into healthcare experience:
1. Longer sales cycles. Custom questionnaires, evidence requests and calls with the buyer’s security team.
2. Higher cost of sale. Senior engineers pulled into security reviews.
3. Lower win rates against certified competitors where HITRUST is a scored criterion.
4. Capped account growth. You can be approved for a pilot but blocked from enterprise-wide rollout.
5. Partner exclusions. Marketplaces and platform ecosystems increasingly set HITRUST as a listing condition for apps handling PHI.
Are there acceptable alternatives?
Sometimes. SOC 2 Type 2 with HIPAA mapping, ISO/IEC 27001, or a HITRUST e1 may be accepted. Always get acceptance of an alternative in writing, ideally as a contract amendment, not as an email from the business sponsor.
Decision guide
| Your situation | Recommended action |
| No demand, healthcare is a minor segment | Monitor. Maintain SOC 2 |
| No demand yet, healthcare enterprise is the growth plan | Readiness assessment now, e1 within 12 months |
| Contract clause with date more than 12 months away | Start scoping now |
| Contract date inside 9 months | Engage assessor immediately, negotiate interim deliverable |
| Certification lapsing within 6 months | Begin recertification fieldwork planning now |
Key takeaways
- There is no legal penalty for lacking HITRUST.
- Contractual, commercial and reputational consequences can be significant.
- Missed deadlines are recoverable if you communicate early with a credible plan.
- Lapsed certification creates misrepresentation and breach of contract risk.
- Certification strengthens your position after an incident.
Frequently asked questions
Is there a fine for not being HITRUST certified?
No. HITRUST is not a legal requirement, so no regulator issues fines for lacking it.
Can a customer terminate my contract over HITRUST?
Yes, if the contract makes certification an obligation and you fail to cure the breach within the agreed period.
What if my HITRUST certification expires?
You must stop representing yourself as certified and may be in breach of contracts that require you to maintain certification.
Can I negotiate more time to get certified?
Often, yes. A dated plan supported by an Authorized External Assessor and an interim deliverable improves your chances.
Does not having HITRUST increase breach liability?
Not directly, but it removes strong evidence of recognized security practices that regulators and courts consider.
About Finstein
Finstein is a HITRUST Authorized External Assessor. Our team includes CCSFP and CHQP qualified HITRUST professionals, CISA certified auditors and ISO 27001 lead auditors, led by Chartered Accountants. We support readiness assessments, validated e1, i1 and r2 assessments, interim assessments and recertification for organisations in the US, India, the UK and the Middle East that serve US healthcare, using an efficient remote delivery model. Get a deadline recovery plan.
#HITRUST #HITRUSTCSF #HITRUSTCertification #HealthcareCybersecurity #HealthcareCompliance #HIPAA #HIPAACompliance #Cybersecurity #DataSecurity #InformationSecurity #RiskManagement #ThirdPartyRisk #VendorRiskManagement #HealthcareIT #HealthTech #PHI #DataPrivacy #Compliance #GRC #CyberRisk #SOC2 #ISO27001 #NIST #BusinessAssociates #HealthcareTechnology